Sign up with Google
 Sign in with Zoho
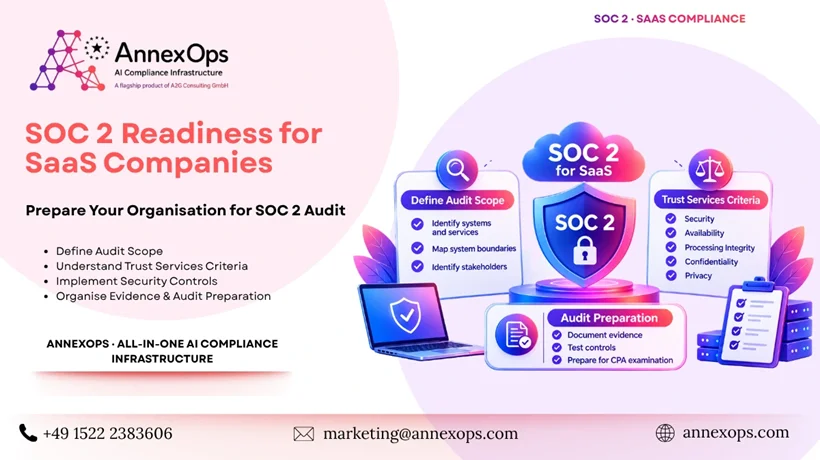
When a business chooses a SaaS provider, it is not only evaluating the software. It is also evaluating how that provider protects customer information, manages access, responds to security incidents and maintains reliable operations.
This is particularly important for SaaS companies working with enterprise customers. Before signing a contract, prospective clients may ask about security policies, data handling procedures, vendor management and independent assurance reports.
SOC 2 is one framework that helps service organisations demonstrate how relevant controls are designed and operated. However, preparing for a SOC 2 examination involves more than writing security policies or completing a checklist. It requires coordination between teams, clear control ownership and reliable documentation.
For SaaS founders and technology leaders, understanding the readiness process early can make security governance more manageable.
What Is SOC 2 and Why Does It Matter?
SOC 2 is an attestation framework developed by the American Institute of Certified Public Accountants (AICPA). It is based on the Trust Services Criteria, which address five areas:
- Security: Protection of systems and information against unauthorised access.
- Availability: Whether systems and services are available for operation and use as agreed.
- Processing Integrity: Whether system processing is complete, valid, accurate, timely and authorised.
- Confidentiality: Protection of information designated as confidential.
- Privacy: How personal information is collected, used, retained, disclosed and disposed of.
Security is the common foundation for a SOC 2 examination. The other categories are included when they are relevant to the organisation's services and commitments.
For a SaaS company, SOC 2 can provide customers with independent information about controls relevant to the services they use. It can also encourage the organisation to establish more consistent internal security practices.
It is important to understand that SOC 2 is not a certification. An independent CPA firm conducts the examination and issues the SOC 2 report.
Why SaaS Businesses Should Prepare Before an Audit
Waiting until a customer requests a SOC 2 report can create unnecessary pressure. Businesses may need to identify missing policies, review access permissions, organise evidence and address control gaps within a limited timeframe.
Starting preparation earlier gives teams more time to understand their current security practices.
There are several reasons why early readiness matters.
1. Enterprise Customer Expectations
Enterprise procurement and security teams often evaluate the security practices of their software suppliers. They may request information about access controls, incident response, business continuity and data protection.
A structured SOC 2 readiness process helps a SaaS company organise the information needed to respond to these assessments.
2. Better Visibility Into Security Controls
As a company grows, its systems and responsibilities become more complex. New employees, applications, integrations and cloud services introduce additional access and operational considerations.
Documented controls help management understand who is responsible for specific security activities and whether those activities are being performed consistently.
3. More Organised Audit Preparation
An examination requires supporting evidence. If evidence is collected only when an auditor requests it, teams may struggle to locate approvals, review records, policies and system logs.
Maintaining documentation throughout normal business operations makes preparation more systematic.
Understanding SOC 2 Type 1 and Type 2
One of the first decisions during SOC 2 planning is understanding which type of examination is appropriate.
Both types assess controls against applicable Trust Services Criteria, but they examine different aspects of control performance.
A Type 1 report may be suitable when an organisation needs an assessment of control design at a particular date. A Type 2 report provides information about how controls operated over a defined period.
The appropriate examination depends on customer expectations, business requirements and the organisation's readiness.
Key Areas to Address Before a SOC 2 Examination
A practical readiness programme should begin with the systems and processes that support the organisation's services.
Define the Audit Scope
The organisation should identify the services, infrastructure, systems, locations and relevant business processes included in the examination.
A clearly defined scope helps prevent confusion about which controls and teams are involved.
Review Access Management
Access to production systems, databases and sensitive information should be managed according to job responsibilities.
Useful practices include:
- Assigning access based on business requirements.
- Removing access when employees leave or change roles.
- Reviewing privileged accounts.
- Maintaining records of access approvals.
- Using appropriate authentication controls.
Establish Incident Management Procedures
Security incidents require defined reporting, investigation and response procedures.
Teams should understand how to identify an incident, notify responsible personnel, document actions and review lessons learned after an event.
Maintain Change Management Records
SaaS products change frequently through software updates, infrastructure modifications and new feature releases.
A structured change management process can document approvals, testing, deployment responsibilities and relevant reviews.
Review Third-Party Providers
SaaS companies often depend on external cloud providers, payment services, analytics tools and other suppliers.
Management should understand which providers support critical services, what information they can access and how relevant supplier risks are reviewed.
Why Evidence Management Is Essential
Evidence is an important part of SOC 2 readiness because documented controls must be supported by records that demonstrate how relevant activities are performed.
Depending on the control, evidence may include:
- Access review records.
- Security policies and approved procedures.
- Incident response documentation.
- Employee training records.
- Change approval records.
- Vendor assessment documents.
- System monitoring records.
- Backup and recovery test results.
Evidence should be accurate, relevant and traceable to the control it supports.
For example, a written access management policy describes the organisation's intended process. An access review record provides additional evidence that the review actually took place.
Keeping these records organised throughout the year reduces the amount of last-minute work required before an examination.
Common SOC 2 Readiness Mistakes
Even organisations with established security practices can face challenges when preparing for an examination.
Treating SOC 2 as a documentation exercise: Policies alone do not demonstrate that controls operate effectively. Teams must follow the documented procedures and retain supporting records.
Starting evidence collection too late: Reconstructing historical activities can be difficult. Evidence should be collected as part of normal operations.
Unclear control ownership: When no individual or team owns a control, reviews and follow-up actions may be missed.
Ignoring third-party dependencies: External providers can affect service security and availability. Their relevance should be considered during risk assessment.
Using the same approach for every Trust Services Criterion: Not every category applies to every service. The organisation should determine which criteria are relevant to its commitments and operations.
How Compliance Software Can Support SOC 2 Readiness
As the number of controls, systems and evidence records increases, managing everything through spreadsheets and email can become difficult.
Compliance software can help organisations maintain a centralised view of their readiness activities. Depending on the solution, useful capabilities may include:
- Mapping applicable Trust Services Criteria to controls.
- Assigning control owners and responsibilities.
- Organising supporting evidence.
- Tracking review and assessment activities.
- Maintaining records across multiple frameworks.
- Monitoring outstanding readiness tasks.
For organisations managing several compliance initiatives, connecting related control records can also reduce unnecessary duplication. However, evidence should only be reused when it genuinely supports the relevant requirement.
AnnexOps provides compliance software that supports SOC 2 control tracking, evidence management and audit preparation. Its workflows help teams organise relevant compliance activities alongside other governance requirements.
Businesses planning their preparation can read this detailed guide to SOC 2 readiness for SaaS companies, which explains audit scope, Trust Services Criteria, control ownership and evidence preparation in greater detail.
Final Thoughts
SOC 2 readiness is not simply a task to complete before an audit. It is an opportunity for SaaS companies to understand their security responsibilities, improve internal processes and establish consistent ways to manage controls.
The most effective preparation begins with a clear scope, defined responsibilities and practical procedures that teams can follow. Evidence collection should remain part of everyday operations rather than becoming a last-minute activity.
By approaching readiness as an ongoing business process, SaaS organisations can build stronger security governance and respond more confidently to customer assurance requirements.