Sign up with Google
 Sign in with Zoho
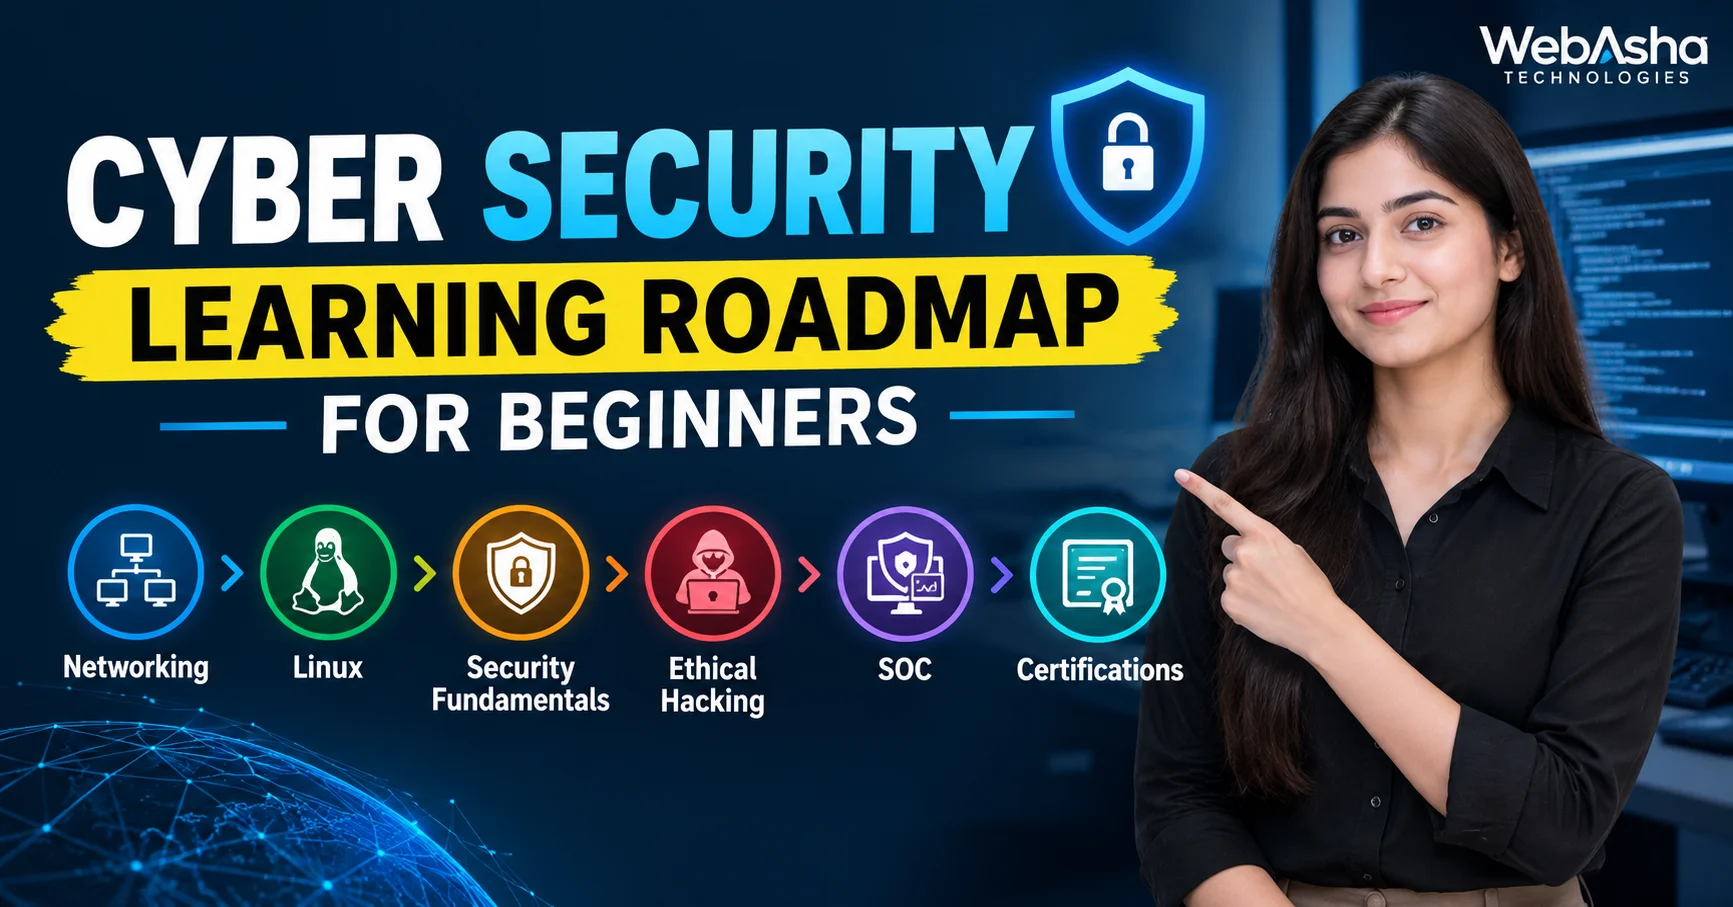
My Practical Cyber Security Learning Roadmap
When I first started exploring cybersecurity, I quickly realized that the field was much bigger than I expected. There were topics such as ethical hacking, Linux, networking, web security, vulnerability assessment, and security operations. The biggest challenge was not finding information; it was deciding what to learn first.
I found that a step-by-step approach makes cybersecurity much easier for beginners.
Start With Networking
I would recommend learning networking before jumping into hacking tools. Start with IP addresses, ports, DNS, TCP/IP, HTTP, HTTPS, routers, and firewalls.
For example, when a security tool reports an open port, knowing what that port represents helps you understand why it may matter.
Learn Linux
Linux is another important foundation. Beginners can start with basic commands, files and directories, users, permissions, processes, services, and logs.
I prefer learning Linux commands through small practical exercises instead of trying to memorize long command lists. Using a command while solving a real task makes it much easier to remember.
Understand Security Fundamentals
Before learning advanced tools, understand authentication, authorization, encryption, hashing, access control, vulnerabilities, threats, and risk.
A simple example is authentication versus authorization. Authentication identifies a user, while authorization determines what that user is allowed to access. This distinction appears in many real applications.
Explore Ethical Hacking and Web Security
After building the basics, beginners can explore ethical hacking in authorized labs. Learn about information gathering, scanning, vulnerability identification, testing, and reporting.
Web security is also worth learning because many organizations depend on web applications. Topics such as authentication, sessions, access control, input validation, injection, and cross-site scripting provide useful practical knowledge.
Always practice security testing only on systems you own or have permission to test.
Practice Vulnerability Assessment
Vulnerability assessment teaches you how to discover and prioritize weaknesses. A simple process is:
Discover → Scan → Validate → Assess → Report → Remediate
The goal is not just to collect scanner results. Understanding the risk and recommending a suitable fix is equally important.
Build Small Projects
Practical work is where cybersecurity knowledge becomes easier to remember. Try building a small Linux lab, analyzing sample network traffic, reviewing logs, or documenting a vulnerability assessment.
For learners looking for structured cybersecurity training with practical learning and projects, the Cyber Security Course from WebAsha Technologies is one learning resource to explore.
Final Thoughts
My recommended learning order is:
Networking → Linux → Security Fundamentals → Ethical Hacking → Web Security → Vulnerability Assessment → Security Operations → Projects
You do not need to learn everything at once. Start with the fundamentals, practice regularly, and gradually move toward the cybersecurity area that interests you most. Consistent hands-on practice can be much more valuable than simply collecting information from different courses and tutorials.