 Sign up with Google
 Sign in with Zoho
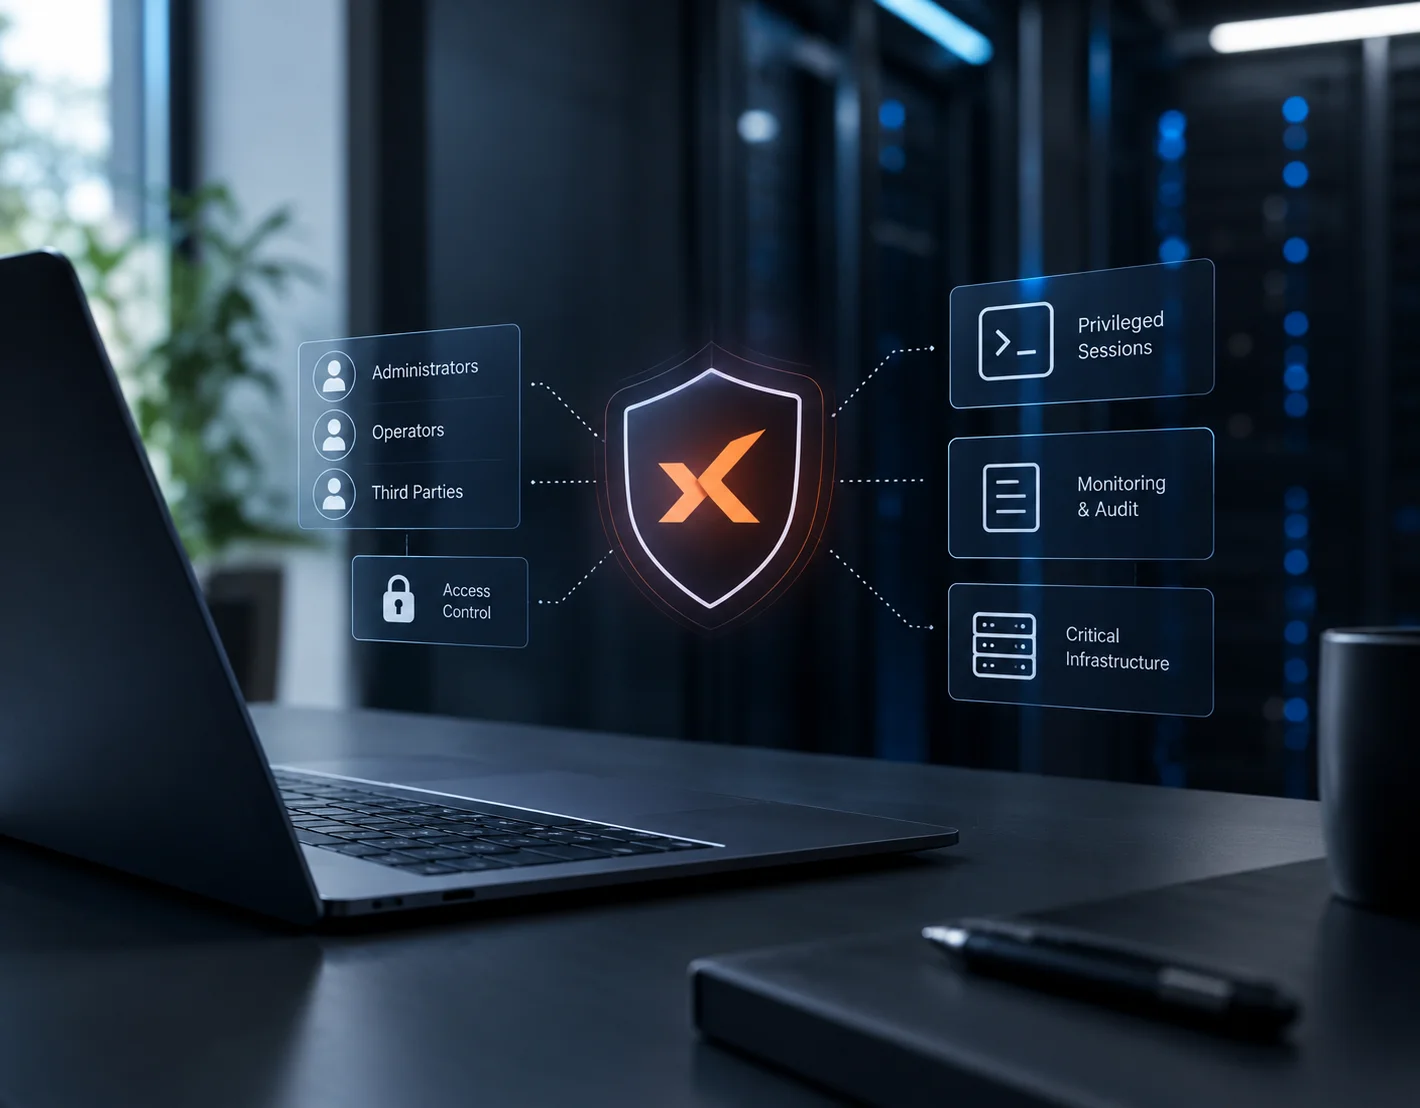
Privileged access is no longer just an administrative concern. In modern IT environments, accounts with elevated permissions can reach servers, network devices, applications, databases, and other critical resources. That makes the way these accounts are controlled an important part of infrastructure security. Privileged access management (PAM) platforms such as WALLIX Bastion are designed around this problem, placing a controlled layer between users and the systems they need to reach.
A WALLIX License defines the scope in which WALLIX Bastion can operate. Rather than being limited to a simple software activation, licensing is connected to the way privileged access is managed within an environment. Depending on the deployment, factors such as users, sessions, access requirements, platform capabilities, and infrastructure size can influence the licensing structure.
This becomes particularly important when looking at environments with strict security requirements. A large enterprise may have internal administrators accessing hundreds of systems, while an industrial or regulated organization may need to control access from a much smaller group of authorized operators. These environments have different operational requirements, so licensing cannot always be considered separately from the access architecture.
One of the more interesting technical aspects is Activating a WALLIX License in restricted environments. Not every infrastructure can maintain a direct connection to external licensing services. Government networks, industrial systems, and isolated security zones may operate without ordinary internet connectivity.
In such cases, the activation process can involve exchanging files rather than maintaining a permanent online connection. Information about the WALLIX deployment is collected into a context file. That information can then be processed through the appropriate licensing workflow, resulting in a signed license file associated with the environment.
The resulting file can be transferred back to the isolated system and applied locally.
The basic concept can be visualized as:
Deployment context → License processing → Signed license file → Local activation → Validation
This approach is useful because the licensing process can accommodate environments where connectivity itself is treated as a security consideration.
Once the platform is operating, the security workflow becomes more significant than the license file itself. Users can request access to designated systems, policies can determine whether that access is permitted, and sessions can pass through the Bastion rather than connecting directly to the target infrastructure.
A simplified access flow looks like this:
Access request → Policy check → Bastion session → Monitoring → Audit
Session management also creates an important source of visibility. Depending on the configuration and licensed capabilities, administrative activity can be monitored and recorded, giving security teams a clearer picture of who accessed a system, when the activity occurred, and which resources were involved.
This is particularly relevant to compliance. Organizations in finance, government, healthcare, industrial operations, and other regulated sectors often need more than authentication alone. They may also need evidence showing how privileged access was granted and how administrative sessions were handled.
Another consideration is scalability. A licensing model that works for a small administrative team may not translate directly to a distributed enterprise with multiple sites and large numbers of privileged sessions. Changes in infrastructure size, access patterns, or security requirements can therefore affect how a WALLIX deployment is structured.
Seen from this perspective, WALLIX licensing is not simply about unlocking software. It sits alongside the broader PAM architecture, connecting technical access requirements with controlled sessions, visibility, auditing, and the operational realities of secure IT environments.